
Online Shopping Scam Alert 2026: How to Spot Fake Websites, Fraudulent Links and Dangerous Apps
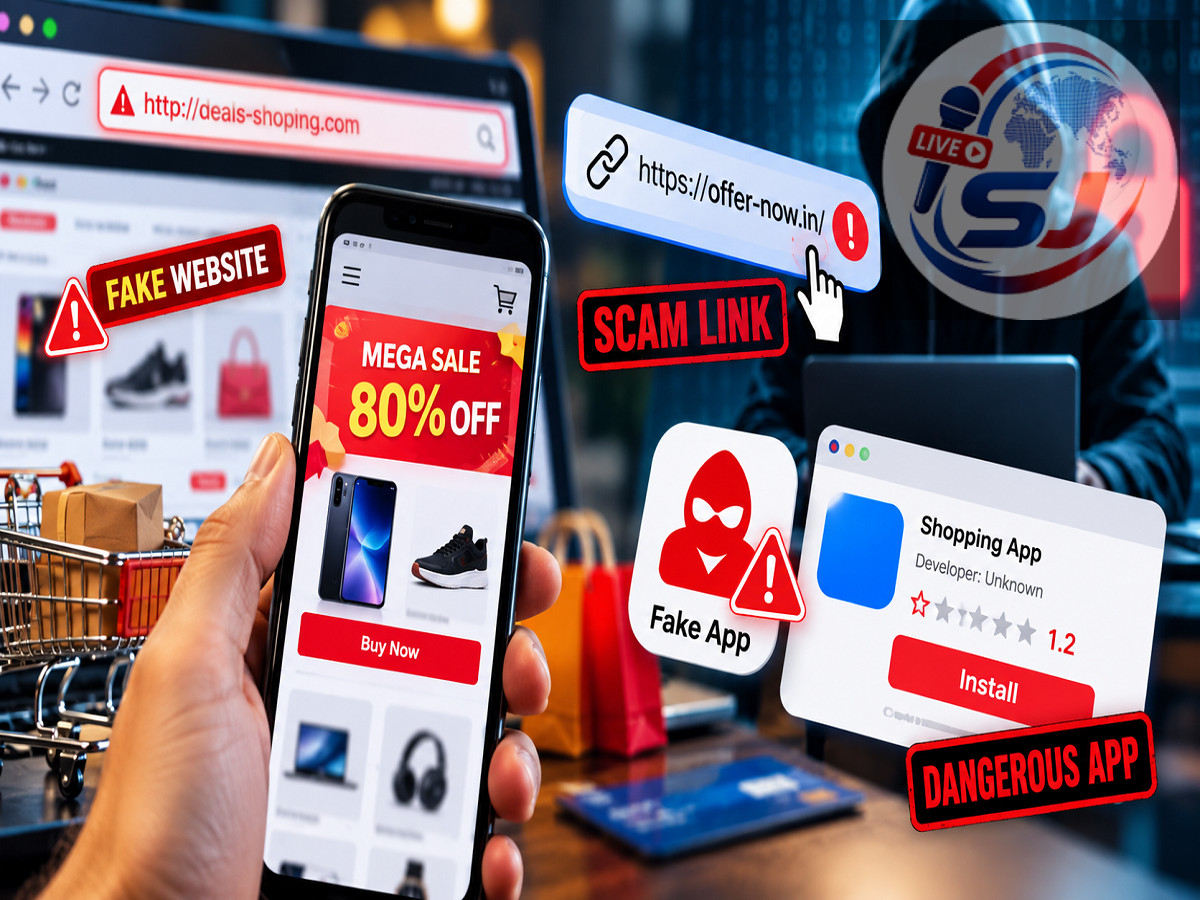
Online Fraud Prevention Tips 2026: Online shopping, digital payments, and mobile applications have made everyday life easier than ever. From purchasing smartphones and clothes to booking tickets and paying bills, millions of people now rely on websites and apps for their daily activities. However, this growing dependence on digital services has also created opportunities for cybercriminals.
Fraudsters are increasingly using fake shopping websites, misleading advertisements, suspicious payment links, and counterfeit mobile applications to steal personal information and money. These fraudulent platforms often resemble genuine websites of well-known companies, making it difficult for ordinary users to identify potential scams.
A tempting discount on an expensive smartphone or an unexpected cashback offer may appear attractive, but clicking an unfamiliar link without verification could expose your banking credentials, passwords, or other sensitive information.
Fortunately, several warning signs can help users identify suspicious websites and applications before becoming victims of online fraud.
Here is a detailed guide to recognising fake websites, avoiding dangerous mobile apps, and protecting yourself from digital scams.
How Do Cybercriminals Use Fake Websites to Steal Money?
Cybercriminals often create websites that closely resemble legitimate shopping platforms, banks, courier services, or government portals.
These websites may use familiar brand colours, logos, product photographs, and layouts to appear trustworthy.
Their primary objective is usually to convince visitors to enter sensitive information, such as login credentials, credit card details, banking passwords, or one-time passwords (OTPs).
Some fraudulent websites collect payments for products that never arrive, while others redirect users to malicious pages or encourage them to download harmful software.
This technique is commonly associated with phishing, where attackers impersonate trusted organisations to obtain confidential information.
Because fraudulent websites can look highly professional, users should not rely on appearance alone when deciding whether a platform is genuine.
1. Examine the Website Address Before Clicking Any Link
One of the simplest ways to identify a potentially fraudulent website is to carefully inspect its web address, also known as the URL.
Scammers frequently register domain names that resemble those of established brands.
For example, a fake shopping website may use an extra word, a different spelling, or a slightly modified domain to imitate a legitimate company.
A fraudulent address might contain unnecessary hyphens, unusual extensions, or additional characters that are easy to overlook.
Before entering personal information or making a payment, check whether the domain matches the company's official website.
Be especially careful with links received through WhatsApp, SMS, email, or social media advertisements.
It is generally safer to open a company's official app or type its verified website address directly into your browser.
Also, remember that a padlock symbol or HTTPS connection does not automatically mean a website is trustworthy. Fraudulent websites can also use encrypted connections.
2. Watch for Unrealistic Discounts and Limited-Time Offers
Online shoppers frequently search for attractive discounts, particularly during festive sales and promotional events.
Cybercriminals take advantage of this behaviour by advertising expensive products at unusually low prices.
For example, a smartphone normally selling for ₹60,000 might appear on an unfamiliar website for just ₹9,999.
Although genuine discounts do exist, extremely low prices on unknown platforms should raise suspicion.
Fraudulent websites may also display countdown timers, limited-stock warnings, or messages claiming that an offer will disappear within minutes.
These tactics are designed to pressure customers into making quick decisions without verifying the seller.
Before purchasing, compare prices with established retailers and check whether the offer is available through the brand's authorised channels.
3. Check Website Design, Language and Business Information
Poor website quality can sometimes indicate a suspicious platform.
Repeated spelling mistakes, inconsistent product descriptions, broken pages, low-resolution images, and unusual payment instructions may suggest that a website has not been professionally maintained.
However, modern scammers can also create convincing websites using sophisticated design tools and artificial intelligence.
Therefore, a polished appearance is not proof of authenticity.
Consumers should also review the website's contact information.
A legitimate online retailer will generally provide relevant business details, customer support options, and policies covering returns, refunds, and deliveries.
If a website provides no verifiable company information or relies only on an unfamiliar email address, proceed carefully.
Even when contact details are displayed, users should verify them independently because scammers can publish fake addresses and phone numbers.
4. Be Careful When Downloading Mobile Applications
Fake mobile applications represent another major online security concern.
Cybercriminals may distribute counterfeit versions of banking apps, shopping platforms, payment services, and utility applications.
These apps can imitate legitimate software while secretly collecting personal information or attempting to obtain access to sensitive smartphone functions.
Some fraudulent apps are promoted through social media advertisements, messaging groups, or websites offering exclusive discounts.
Users should avoid installing applications through unfamiliar APK files or unsolicited download links.
Downloading apps from official platforms such as Google Play or Apple's App Store generally provides additional security checks, although no app marketplace can guarantee that every application is completely safe.
Before installation, verify the developer's identity, application details, and official publisher information.
5. Review App Permissions Before Allowing Access
Mobile applications often request permission to access certain smartphone features.
For example, a camera application may need access to the camera, while a navigation service may require location information.
However, unnecessary permission requests can be a warning sign.
If a basic shopping application asks for access to call logs, SMS messages, contacts, or other unrelated information, users should question why those permissions are required.
Some malicious applications attempt to misuse sensitive permissions to collect information or interfere with device security.
Android and iPhone users can review app permissions through their smartphone settings.
Permissions that are unnecessary for an application's main function should be denied or restricted wherever possible.
6. Do Not Trust App Ratings and Reviews Blindly
Many users assume that applications with high ratings are automatically safe.
Unfortunately, fake reviews and manipulated ratings can make suspicious applications appear more reliable than they actually are.
Before downloading an unfamiliar app, examine its reviews carefully.
Look for repeated complaints about unexpected charges, login problems, suspicious permission requests, or difficulty contacting customer support.
Also check the developer's publishing history and whether the application is associated with a verified business.
A large download count may indicate popularity, but it does not independently establish security.
Similarly, a newly released application is not necessarily fraudulent.
Users should consider multiple indicators rather than relying on a single rating or review.
7. Keep Google Play Protect Enabled on Android Phones
Android users have access to Google Play Protect, a built-in security feature designed to help detect potentially harmful applications.
Google Play Protect checks installed applications and can warn users about software that may pose security risks.
To review its status, open the Google Play Store, tap your profile icon, and select Play Protect.
From there, users can check whether scanning is enabled and review available security alerts.
Keeping Play Protect active can provide an additional layer of protection, particularly against known malicious applications.
However, it should not be treated as a replacement for careful downloading habits, software updates, and permission management.
8. Never Share OTPs, Banking PINs or Passwords
One of the most important rules of online safety is to keep confidential financial information private.
Banks and legitimate payment providers do not require customers to disclose their ATM PIN, UPI PIN, or account password to receive refunds or complete routine customer support requests.
Scammers may impersonate delivery agents, bank representatives, or customer service employees and ask users to share OTPs.
They may claim that verification is necessary to process a refund, activate an account, or prevent a payment failure.
Such requests should be treated with suspicion.
Users should never enter banking credentials on websites reached through unexpected messages.
For UPI transactions, remember that entering a UPI PIN normally authorises a payment rather than receiving money.
9. What Should You Do If You Click a Suspicious Link?
Clicking a suspicious link does not automatically mean that your smartphone has been compromised.
However, users should avoid entering information, downloading files, or approving permissions on unfamiliar pages.
If you have already entered a password, change it immediately through the genuine service and enable multifactor authentication wherever available.
If banking information has been exposed, contact your bank using its official customer support channel.
Anyone who has installed a suspicious application should remove it, review device permissions, update the operating system, and perform an appropriate security scan.
If money has been stolen, report the incident as quickly as possible.
In India, victims of financial cybercrime can contact the national cybercrime helpline at 1930 or submit a complaint through the official National Cyber Crime Reporting Portal at cybercrime.gov.in.
Prompt reporting may improve the chances of financial institutions taking timely action, although recovery of stolen funds is not guaranteed.
How to Stay Safe While Shopping Online
A few practical habits can significantly reduce the risk of becoming a victim of online fraud.
-
Use verified websites and official shopping applications.
-
Avoid clicking unexpected links received through messages or emails.
-
Compare unusually attractive offers with prices on trusted platforms.
-
Review seller information, return policies, and customer feedback.
-
Keep your smartphone and applications updated.
-
Enable multifactor authentication on important accounts.
-
Avoid sharing passwords, OTPs, or UPI PINs.
-
Check payment confirmations and bank statements regularly.
These precautions are especially useful during major online sales, when fraudulent promotions may appear alongside genuine advertisements.
Conclusion
Online fraud is becoming increasingly sophisticated, and cybercriminals are using convincing websites, fake mobile applications, and misleading advertisements to target unsuspecting users.
However, identifying suspicious domain names, checking application permissions, verifying business information, and avoiding unrealistic offers can help reduce the risk of financial loss.
The most effective protection against online scams is to verify before you click, download, or pay.
Whether you are purchasing a product, installing a new application, or responding to a payment request, spending a few extra moments checking authenticity can help protect your money, personal information, and digital identity.